CYBERSECURITY & RESILIENCE
Enterprise Zero-Trust Cyber Security & Managed SOC Solutions
Fortify global digital perimeters, eliminate identity vulnerabilities, automate continuous threat intelligence, and guarantee regulatory compliance with end-to-end zero-trust architecture.
- Zero-Trust Architecture
- Managed Cloud SOC
- Microsoft Sentinel SIEM
- Identity Governance
- Continuous Compliance
- 24/7 Incident SLA
STRATEGIC PERSPECTIVE
The Strategic Imperative for Zero-Trust Enterprise Security
Strategic Imperative: Legacy perimeter firewalls and castle-and-moat security models cannot protect modern distributed enterprises. Modern defense demands assuming breach, verifying explicitly, and enforcing least privilege.
As enterprise applications migrate to multi-cloud environments and workforces operate across distributed global endpoints, traditional network perimeter defenses have become completely obsolete. Advanced persistent threats (APTs), credential compromise, and sophisticated ransomware attacks bypass legacy firewalls with ease. A single compromised remote identity or misconfigured cloud storage bucket can trigger catastrophic corporate data breaches, regulatory penalties, and reputational collapse.
Routeget Technologies designs, deploys, and operates comprehensive Zero-Trust cybersecurity architectures. Grounded in the principle of ‘never trust, always verify,’ our solutions ensure that every access request—whether originating inside or outside corporate networks—is explicitly authenticated, authorized within context, and cryptographically inspected before access is granted.
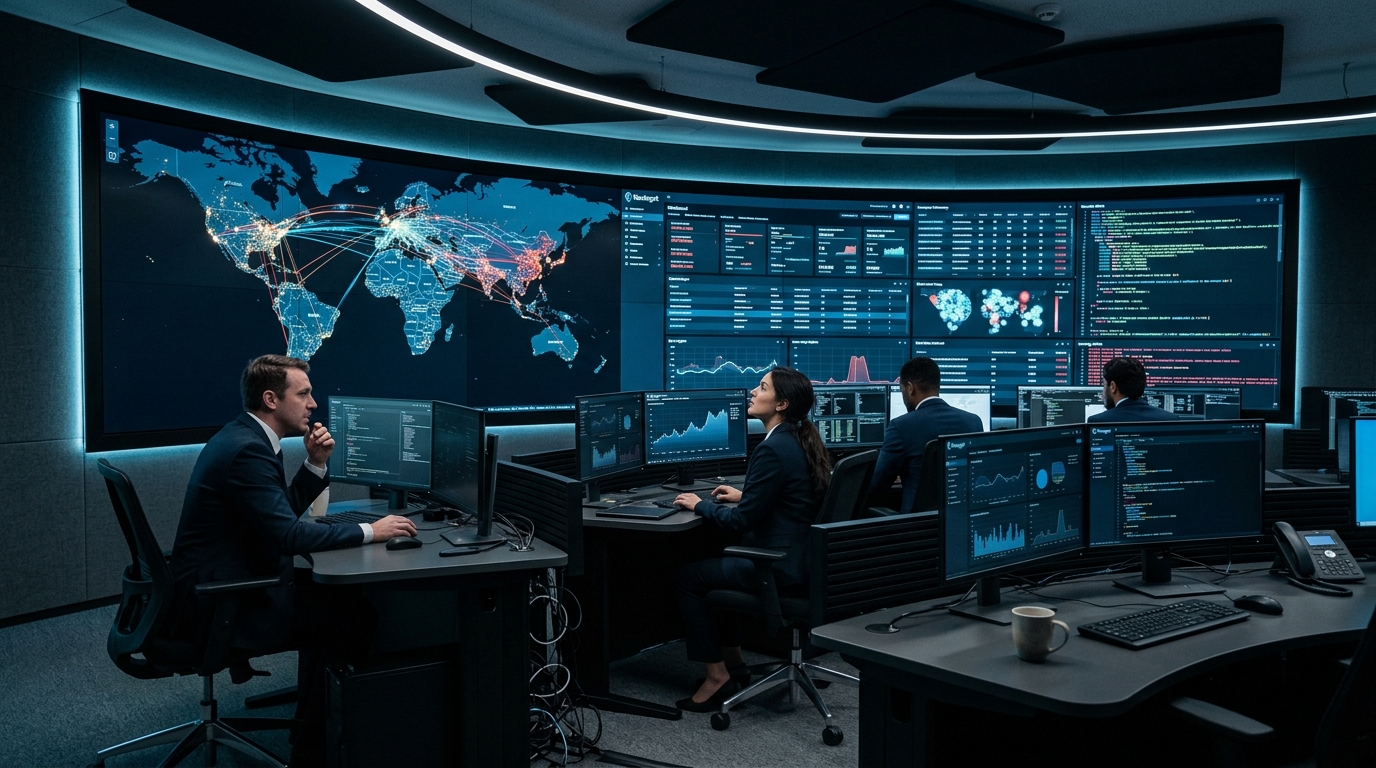
Through our global 24/7/365 follow-the-sun Security Operations Center (SOC) powered by Microsoft Sentinel and Microsoft Defender XDR, we provide continuous threat surveillance, automated incident containment, and forensic breach analysis. We transform cybersecurity from a reactive cost center into an agile business enabler that preserves corporate trust and regulatory compliance.
CORE ARCHITECTURAL PILLARS
Core Zero-Trust Cybersecurity Pillars & Managed Defense
Our cybersecurity practice delivers end-to-end protection across identities, endpoints, cloud workloads, network perimeters, and regulatory compliance.
Identity Perimeter
Identity & Access Governance (IAM)
Enforce strict identity-first security with multi-factor authentication, risk-based conditional access, and automated privileged access management (PAM).
Pillar 01 Scope & Governance
Threat Intelligence
Cloud-Native SIEM & AI-Driven SOC
Deploy Microsoft Sentinel to ingest, correlate, and analyze millions of enterprise security telemetry events with autonomous AI threat detection.
Pillar 02 Scope & Governance
Workload Protection
Cloud Workload & Container Security (CWPP)
Protect multi-cloud virtual machines, Kubernetes clusters, serverless functions, and container registries against zero-day exploits.
Pillar 03 Scope & Governance
Data Governance
Information Protection & Data Loss Prevention (DLP)
Discover, classify, and protect sensitive corporate data across emails, cloud storage, and endpoint devices using Microsoft Purview.
Pillar 04 Scope & Governance
Network Security
Zero-Trust Network Access & SASE
Replace vulnerable legacy VPNs with Secure Access Service Edge (SASE) architectures providing micro-segmented, direct-to-app access.
Pillar 05 Scope & Governance
Audit Readiness
Continuous Regulatory Compliance & Auditing
Maintain continuous compliance posture across ISO 27001, SOC 2 Type II, HIPAA, GDPR, PCI-DSS, and NIST cybersecurity frameworks.
Pillar 06 Scope & Governance
TECHNICAL SPECIFICATIONS & SLA COMMITMENTS
Detailed Architecture Specifications & Delivery Governance
Comprehensive functional requirements, implementation guardrails, and enterprise SLA obligations across all operating pillars.
Identity & Access Governance (IAM) — Detailed Specifications
- Microsoft Entra ID Privileged Identity: Enforce just-in-time (JIT) access, time-bound approvals, and multi-factor authentication for sensitive administrative roles.
- Risk-Based Conditional Access: Dynamically evaluate user location, device compliance, and sign-in risk signals before granting application access.
- Automated User Lifecycle Provisioning: Streamline employee onboarding and immediate offboarding across all corporate apps using SCIM protocols.
Cloud-Native SIEM & AI-Driven SOC — Detailed Specifications
- Hyperscale Log Ingestion: Ingest security logs across Azure, AWS, GCP, on-premise firewalls, and SaaS applications without performance bottlenecks.
- Automated SOAR Playbooks: Implement automated incident response workflows that isolate compromised endpoints and disable rogue accounts in seconds.
- Proactive Threat Hunting: Continuous forensic analysis by certified cybersecurity analysts utilizing global threat intelligence feeds.
Cloud Workload & Container Security (CWPP) — Detailed Specifications
- Vulnerability Management: Continuously scan virtual machine images and container registries for known CVEs and misconfigurations.
- Runtime Threat Detection: Detect anomalous process execution, unauthorized network connections, and privilege escalation attempts in real time.
- Infrastructure-as-Code (IaC) Scanning: Integrate automated security checks into CI/CD pipelines to prevent misconfigurations from reaching production.
Information Protection & Data Loss Prevention (DLP) — Detailed Specifications
- Automated Sensitivity Labeling: Apply cryptographic encryption and access restrictions automatically based on detected content (credit cards, PII, IP).
- Endpoint DLP Enforcement: Prevent unauthorized copying of sensitive corporate files to USB drives, personal cloud storage, or unapproved printers.
- Insider Risk Telemetry: Detect anomalous data hoarding, abnormal bulk downloads, and potential IP theft prior to employee departures.
Zero-Trust Network Access & SASE — Detailed Specifications
- Application Micro-Segmentation: Restrict user connectivity exclusively to the specific application authorized, preventing lateral network movement.
- Cloud Access Security Broker (CASB): Monitor and enforce security policies across unsanctioned shadow IT cloud applications.
- Distributed Denial of Service (DDoS) Defense: Protect public digital perimeters with automated hyperscale traffic scrubbing and web application firewalls (WAF).
Continuous Regulatory Compliance & Auditing — Detailed Specifications
- Real-Time Compliance Scorecards: Continuously track organizational security controls against major global regulatory benchmarks.
- Automated Evidence Collection: Export audit-ready documentation and access logs required by external compliance examiners with one click.
- Third-Party Vendor Risk Assessment: Evaluate and monitor the security posture of external suppliers, partners, and cloud SaaS vendors.
DELIVERY METHODOLOGY
The Routeget XDRI™ Cybersecurity Modernization Lifecycle
Our structured four-stage methodology establishes resilient zero-trust defenses tailored to your corporate operational environment.
Stage 01: eXplore
Threat Modeling & Compromise Assessment
We perform forensic vulnerability scans, evaluate active directory health, assess identity risks, and model threat vectors against MITRE ATT&CK.
Stage 02: Design
Zero-Trust Architecture & Policy Blueprints
Our certified security architects blueprint identity perimeters, conditional access rules, SIEM ingestion topologies, and incident response playbooks.
Stage 03: Realize
Iterative Security Rollout & Red-Team Verification
We implement Microsoft Sentinel, deploy Defender XDR agents, configure DLP policies, and conduct simulated red-team penetration attacks.
Stage 04: Impact
24/7 Managed SOC, Telemetry & Continuous Governance
We transition operations to our global follow-the-sun SOC, monitor threat telemetry around the clock, and conduct quarterly compliance reviews.
QUANTIFIABLE IMPACT
Validated Security Outcomes Across Enterprise Deployments
Our cybersecurity implementations produce measurable risk reduction and validated compliance benchmarks.
Rapid threat identification powered by AI-driven Microsoft Sentinel correlation engines.
Automated SOAR playbook execution isolating compromised assets before lateral spread occurs.
Comprehensive eradication of password-only attack vectors through phased passwordless MFA deployment.
Verified compliance posture maintained across ISO 27001, SOC 2, HIPAA, and GDPR standards.
EXECUTIVE FAQ
Enterprise Cybersecurity Frequently Asked Questions
Key architectural, operational, and commercial insights answered by our Principal Security Architects and CISOs.
What is the difference between traditional perimeter defense and Routeget's Zero-Trust architecture?
How does Routeget's Managed SOC integrate with our existing internal IT team?
Can Routeget help us achieve and maintain ISO 27001 or SOC 2 Type II certification?
How quickly can Routeget deploy Microsoft Sentinel across our multi-cloud enterprise estate?
ENTERPRISE TRANSFORMATION
Strengthen Your Enterprise Cyber Defenses Today
Consult with Routeget’s Principal Security Architects to schedule a confidential compromise assessment, evaluate zero-trust maturity, and explore Managed SOC options.
